
THANK YOU FOR TAKING PART!
Thank you to everyone who made meshcloud Con ’26 such a special experience! Seeing so many new connections, thoughtful conversations, and shared insights come to life over these days was truly inspiring.
A special thank you to our speakers from EDEKA IT, Deutsche Rentenversicherung Bund, Markant, Bechtle, RheinEnergie, Denkmit, microfin, Liquid Reply, cc cloud – your insights sparked meaningful conversations and made the event truly memorable.
We’re also grateful to Enclaive, STACKIT, Computacenter and AWS for their support in making meshcloud Con ’26 possible!
HIGH-SIGNAL EVENT FOR REAL PLATFORM DECISIONS
Hear unfiltered platform stories.
Join practitioner-led sessions.
Gather ideas you can apply to your own platform.
24 September, 9am - 5pm
Attend the full-day conference in Atelier Lihotzky, Frankfurt am Main
-
Danziger Platz 12, 60314 Frankfurt am Main-Bornheim/Ostend
Pre-Conference Dinner
23 September, 6 - 10pm
Danzig am Platz, Frankfurt am Main
-
Ostparkstraße 11, 60314 Frankfurt am Main-Bornheim/Ostend
09:00-10:30 — TALKS
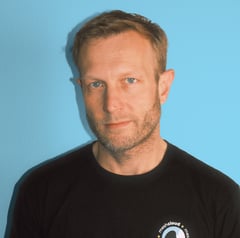
JÖRG GOTTSCHLICH
CEO, meshcloud
Welcome Speech

HARALD JOOS
Deutsche Rentenversicherung Bund
Strengthening Europe’s Digital Sovereignty: Opportunities, Risks, and Strategies Beyond Black-and-White Debates
This session breaks down the three pillars of sovereignty – Private, Public, and Sovereign Cloud – and how to steer them. Discover how to use open standards and KPIs to build a resilient, multi-cloud stack that safeguards Europe’s digital autonomy


BENJAMIN
FLAVEN-STEIN, PASCAL PETSCH
FLAVEN-STEIN, PASCAL PETSCH
Markant
Impacting DevEx, Costs, and Sovereignty with an Internal Developer Platform
High complexity and rising costs demand a smarter approach to DevOps. This session breaks down the creation of an Internal Developer Platform (IDP) centered on the "Thinnest Valuable Platform" (TVP). Optimize DevEx and digital sovereignty across hybrid clouds without overloading teams.
10:30-11:00 — COFFEE BREAK & MESHSTACK DEMO
11:00-12:10 — TALKS

MAX KÖRBÄCHER
Liquid Reply
We Need to Evolve Our Platforms to Support Agentic AI
Autonomous agents break traditional platform engineering by generating their own logic and thriving on unpredictable workloads. While Kubernetes remains the baseline, supporting these AI agents requires a completely new infrastructure blueprint. This session explores the technical pillars of an agentic runtime, from kernel-level sandboxing to cognitive memory fabrics and fractional GPU scheduling. Discover why static RBAC must give way to Intent-Based Access Control (IBAC) to secure the "Somehow" Era.


MICK BECKER, MARKUS VON STRUENSEE
EDEKA IT
Platform on Platform: How EDEKA IT Scales Through Decentralized Self-Service
How do you scale when your organization triples in size and accelerates its cloud migration without growing the platform team? This session explores how EDEKA IT evolved from manual ticketing bottlenecks to a decentralized self-service platform model. What started as an effort to improve cloud access grew into a foundation that enabled other expert teams to provide their own services through the same platform. Join Mick and Markus to learn how EDEKA IT is balancing developer autonomy, governance, and scale across a growing organization.

MANUEL
ZAPF
ZAPF
cc cloud
Bare Metal Platform Engineering with Harvester and Rancher
This talk explores how a private cloud platform built with Harvester and Rancher enabled consistent operations across virtual machines and containers while improving standardisation and infrastructure utilisation. Discover the architectural decisions, trade-offs, and practical lessons learned from running real workloads at scale.

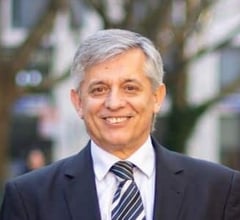
ROBERT SPECHT, ANASTASIOS PAPAKOSTAS
Enclaive
Lightning talk "The Dilemma of Regulated Industries"
Financial services, healthcare, and public sector organizations need AI and cloud platforms but regulations often prevent them from processing sensitive data in the public cloud. In this session, Robert will show how meshStack and enclaive combine platform engineering with confidential computing to solve this dilemma. See how development teams provision secure cloud environments through self-service, while Trusted Execution Environments protect data in use without requiring application changes. Learn how platform teams automate governance and enable sovereign cloud adoption without sacrificing the agility of hyperscalers.
12:10-13:10 — LUNCH & MESHSTACK DEMOS
13:10-14:00 — PANEL DISCUSSION


JULIA PERGANDE (microfin),
ANDRÉ ALFTER (Bechtle)

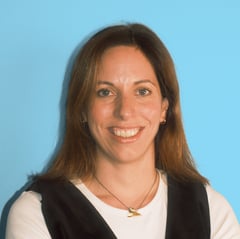
ERIK SCHUBERT (RheinEnergie), CHRISTINA KRAUS (meshcloud)
Minimum Viable Sovereignty: How Much Control Do You Actually Need?
Full sovereignty over the entire cloud stack isn't realistic and in most cases, it isn't necessary. This panel moves past sovereignty as a buzzword to focus on a practical target: Minimum Viable Sovereignty – the baseline of control an organization cannot fall below without losing its ability to act independently.
Bringing together an enterprise strategy lead, a regulatory advisor, a public sector platform engineer, and a vendor representative, this session tackles the hard operational reality of cloud independence. Discover which workloads truly need crown-jewel protection, how to audit hidden dependencies inside management planes and SaaS tooling, and how to build measurable control without grinding digitalization to a halt.
14:00-15:00 — WORKSHOPS
LUKAS WEBERRUSS
STACKIT
STACKIT Landing Zones: From Request to Sovereign Cloud Environments
This hands-on workshop dives deep into designing and implementing STACKIT Landing Zones, showing you how to build a highly secure, well-governed infrastructure that natively satisfies modern compliance and data residency rules. In just 1 hour, you’ll master STACKIT’s resource hierarchy, and walk away ready to deliver self-service environments that your developers love and your compliance officers trust.
CHRISTIAN SCHREINER (Computacenter), YOUNG-HWAN KIM (meshcloud)
AWS Sovereign Cloud
The AWS European Sovereign Cloud promises operational isolation and strict data residency without sacrificing public cloud agility. But how do platform teams make sovereign infrastructure frictionless for engineering teams? In this interactive workshop, you'll walk through the practical mechanics of landing zones, identity isolation, and governance for sovereign AWS environments. Learn how to build automated guardrails that satisfy strict EU compliance standards while keeping cognitive load low and developer velocity high.
FLORIAN NOWARRE, ANDREAS GRUB
meshcloud
One-click K8s-Platform on STACKIT
Standardizing Kubernetes infrastructure across enterprise teams shouldn't lead to IaC ticket backlogs or snowflake configurations. In this practical, hands-on workshop, the meshcloud team will show you how to transform raw STACKIT Kubernetes Engine (SKE) infrastructure into a full-fledged Internal Developer Platform. Learn how to bundle essential building blocks like namespaces, RBAC, CI/CD pipelines, and landing zones into reusable, one-click Golden Paths.Walk away with proven reference architectures and actionable tools to give your application teams self-service sovereign K8s without sacrificing platform control.
15:00-15:30 — COFFEE BREAK & MESHSTACK DEMOS
15:30-16:00 — TALK
JOHANNES RUDOLPH
meshcloud
Talk
"Agentic Platform Engineering"
YOLO'ing code got cheap, but building the confidence to deploy to it to prod did not. Applying agents to platform engineering work hits different than software engineering. Reconciling infrastructure changes is slow and the stakes are high. When the only thing between your agent and your production database is a line in AGENTS.md, you should join this session. Johannes will not only share how to make agents safe, but also how they make platform engineering fun again.
16:00-16:30 — AWARD CEREMONY & RAFFLE
16:30 — POST-EVENT DRINKS
SOVEREIGN PLATFORM ENGINEERING
Sovereign Platform Engineering is the central theme of meshcloud Con ’26. It explores how organizations design, build, and operate platform architectures that enable autonomy, control, and scalability in increasingly complex multi-cloud environments.
To make this topic tangible, the conference is structured into two complementary tracks combining talks and workshops:
Platform Technology
This track covers how platforms are built and operated in practice, including:
- AI Platforms
- Agentic AI
- Internal Developer Platforms & Golden Paths
- GitOps Security and Landing Zones
- Automation & Developer Self-Service
- Multi-Cloud Implementations
- Kubernetes
- Observability
Business & Strategy
This track explores how platform teams create value and scale impact across organizations, including topics such as:
- Sovereign Clouds
- Platform Organizations
- Platform as a Product
- Platform vision and ownership
- FinOps & Cost Management
- Developer Experience
What you'll get from meshcloud Con '26
Keynotes grounded in real experience
Speakers kick off the day with insights from building and running platforms in practice
Workshops that go beyond theory
Hands-on discussions and deep dives into real platform obstacles — with space to ask, challenge, and contribute
Decisions you take back to your team
Leave with concrete ideas, patterns, and approaches you can apply in enterprise environment
Meaningful conversations with peers
Exchange ideas with platform teams, speakers, and experts — without the noise of large-scale events
Impressions from meshcloud Con 2024-2025
This event is supported by